Remote and hybrid work have changed how organizations manage access to corporate applications, business data, and internal networks. Employees, contractors, and third-party vendors now connect from different locations and devices, making secure remote access a critical part of enterprise cybersecurity.
For years, Virtual Private Networks (VPNs) have been a standard solution for remote connectivity. However, traditional VPN architectures can introduce security and operational challenges, particularly when organizations need to protect distributed users, cloud applications, and sensitive business information.
This is where Zero Trust Network Access (ZTNA) comes in. Built on the principle of never trust, always verify, ZTNA evaluates access requests based on identity, context, and security policies rather than automatically trusting users because they have connected to a corporate network.
As businesses adopt cloud services and distributed work models, VPN alternative ZTNA is becoming an important consideration for organizations looking to strengthen access security while simplifying remote connectivity.
In this blog, we explore the limitations of traditional VPNs, how ZTNA works, the key differences between the two approaches, and when businesses should consider making the transition.
-
What limitations of traditional VPNs are driving organizations to consider alternatives?
Traditional VPNs were designed primarily to establish encrypted connections between remote users and corporate networks. While they still serve a purpose, their network-centric approach may not align with modern enterprises’ security requirements.
Several limitations are driving organizations to explore alternatives.
Broad network access increases security risks
Many traditional VPN deployments provide users with access to a corporate network segment after authentication. Depending on the configuration, this can expose more resources than users need for their jobs.
If an attacker compromises a user’s credentials or device, the resulting connection may create opportunities to access other systems within the reachable network.
ZTNA addresses this challenge by limiting access to explicitly authorized applications and resources.
Compromised credentials can expose critical resources
VPN authentication alone does not guarantee that a user or device remains trustworthy throughout a session. Stolen credentials, phishing attacks, and compromised endpoints can allow unauthorized individuals to exploit legitimate remote connections.
Organizations need access controls that consider more than a successful login. User identity, device posture, contextual signals, and access policies can help determine whether a connection should be permitted.
Managing remote access becomes complex
As organizations expand across offices, cloud environments, and remote locations, maintaining VPN infrastructure can become operationally demanding. VPN gateways, capacity planning, access policies, and troubleshooting may require additional IT resources.
A growing number of users and applications can further complicate access management, especially when employees need reliable connectivity from different locations.
Cloud adoption changes network access requirements
Modern enterprises increasingly rely on SaaS platforms, cloud-hosted workloads, and applications distributed across multiple environments. Routing all remote traffic through a corporate VPN gateway may introduce unnecessary network complexity or affect application performance, depending on the architecture.
A more application-centric access model can help organizations provide direct, policy-controlled connectivity to authorized resources.
Third-party access creates additional challenges
Partners, vendors, consultants, and contractors often require access to specific business applications. Granting broader network access than necessary can increase the attack surface.
Organizations need a way to provide these users with access to approved resources without unnecessarily exposing internal networks.
These limitations do not mean that every VPN deployment is insecure or obsolete. Properly configured VPNs can still provide valuable protection. However, organizations seeking more granular, identity-aware access controls may find ZTNA better suited to their evolving requirements.
-
How does ZTNA provide secure access without traditional VPN architecture?
Zero Trust Network Access (ZTNA) takes a different approach to remote access. Instead of connecting users to a broader corporate network, it establishes controlled access to specific applications and resources based on defined security policies.
The approach aligns with the principles outlined in the National Institute of Standards and Technology (NIST) Zero Trust Architecture framework, which emphasizes resource protection, identity verification, and least-privilege access.
Here is how ZTNA strengthens remote access security.
Identity-based authentication and authorization
ZTNA verifies a user’s identity before granting access to an application. Depending on the solution and configuration, this may involve integration with an identity provider, multifactor authentication, and other identity verification mechanisms.
Access is granted according to the user’s role, permissions, and applicable security policies. A successful login does not automatically authorize access to every resource on the network.
Application-level access instead of network-wide access
ZTNA follows the principle of least privilege. Users receive access only to the applications they are authorized to use.
For example, a finance employee may need access to an accounting application but not to engineering systems or other internal resources. ZTNA policies can restrict access accordingly, reducing unnecessary exposure.
Device posture and contextual checks
ZTNA solutions can evaluate device security posture and other contextual factors before granting access. Depending on the implementation, checks may include device compliance, operating system status, user identity, and location-related signals.
These checks help organizations make access decisions based on more than credentials alone.
Reduced exposure of internal applications
With an appropriately designed ZTNA architecture, internal applications do not need to be broadly exposed to remote users through traditional network access.
Instead, access is mediated through the ZTNA solution’s control and enforcement mechanisms. Users can connect to approved applications without receiving general access to the underlying network.
This helps reduce the attack surface and limits opportunities for lateral movement if an account or device is compromised.
Improved visibility into access activity
ZTNA can provide security teams with visibility into application access, connection attempts, user activity, and policy enforcement, depending on the platform’s capabilities.
This information helps administrators review access patterns, investigate suspicious activity, and refine security policies.
In short: ZTNA changes the focus from securing a connection to a network to securing access to an individual resource. It enables organizations to apply granular access policies across remote, on-premises, and cloud environments without relying on a traditional VPN architecture.
-
What are the key differences between ZTNA and VPN-based access?
Although both technologies can support secure remote access, they differ in how they establish trust, grant permissions, and protect enterprise resources.
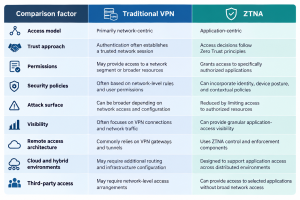
Note: Actual capabilities depend on the product, deployment architecture, and configuration. VPNs can also enforce granular controls, and ZTNA deployments vary in their verification and monitoring capabilities.
Why does application-level access matter?
Consider a third-party vendor who needs to access one internal application to troubleshoot a business issue.
With a conventional VPN setup, the vendor may be granted access to a network segment containing that application and potentially other reachable resources, depending on the access policies.
With ZTNA, the organization can authorize access specifically to the required application while restricting access to unrelated resources. This follows the principle of least privilege and can reduce the potential impact of compromised credentials.
The difference becomes especially important when organizations manage large numbers of remote users, external partners, cloud applications, and sensitive internal systems.
Does ZTNA completely replace VPNs?
Not necessarily. ZTNA is a strong alternative for application-level remote access, but some environments still require network-level connectivity for legacy applications, specialized protocols, or particular infrastructure requirements.
Organizations should evaluate their application portfolio, connectivity requirements, and existing security controls before deciding whether to replace VPNs entirely or adopt a phased transition.
-
When should businesses consider ZTNA as a VPN alternative?
ZTNA can be a practical choice for organizations that want to modernize remote access while strengthening control over who can access their business applications.
Here are some situations in which businesses should consider adopting ZTNA as a VPN alternative.
- When supporting a remote or hybrid workforce
Organizations with employees working from home, branch offices, or multiple locations need secure and consistent access to business applications.
ZTNA allows organizations to apply access policies based on user identity and permissions rather than relying solely on network location. This helps support distributed teams without automatically extending broad network access to every remote user.
- When moving applications to the cloud
As businesses adopt SaaS platforms, cloud-hosted workloads, and hybrid infrastructure, traditional network-centric access models can become more complicated to manage.
ZTNA provides an application-centric approach that can support access to resources across on-premises and cloud environments. This helps organizations apply consistent access policies as their infrastructure evolves.
- When strengthening protection against credential theft
Phishing, stolen credentials, and compromised endpoints can undermine remote access security.
Organizations looking to reduce their dependence on a single authentication event should consider ZTNA solutions that support additional identity verification, device posture assessment, and contextual access policies.
These controls can help restrict unauthorized access even when an attacker obtains valid credentials.
- When providing access to vendors and third parties
External users often need access to selected business applications for support, maintenance, or collaboration.
ZTNA enables organizations to define application-specific permissions for employees, contractors, and vendors. This can reduce the need to provide broad network access to people outside the organization.
- When improving access visibility and control
Security teams need to understand which users are accessing which applications and whether access policies are being followed.
Organizations that want more detailed application-level visibility should evaluate ZTNA platforms with centralized policy management, access monitoring, audit trails, and reporting capabilities.
- When simplifying remote access management
Managing VPN gateways, remote connectivity, and access policies across a growing workforce can add operational complexity.
A suitable ZTNA platform can help centralize access management and reduce dependence on traditional VPN infrastructure. Businesses should assess deployment requirements, integration with existing identity systems, application compatibility, user experience, and total cost of ownership before making a decision.
How can businesses transition from VPN to ZTNA?
A phased approach can help organizations move to ZTNA without disrupting business operations.
- Identify critical applications: Map the applications, users, devices, and external parties that require remote access.
- Review existing VPN access: Identify users with broad permissions and applications that need tighter access controls.
- Define Zero Trust policies: Establish application-specific permissions based on user roles, device security, and business requirements.
- Run a pilot deployment: Start with a defined group of users or applications and validate security, performance, and compatibility.
- Expand in phases: Monitor results, refine policies, and migrate additional applications as the organization becomes ready.
This approach allows businesses to validate the benefits of ZTNA while maintaining access to applications that still depend on VPN connectivity.
Conclusion: Strengthen Remote Access Security with Seqrite ZTNA
Traditional VPNs remain useful for many remote access scenarios, but their network-centric architecture may not provide the level of application-specific control and visibility that modern enterprises require.
ZTNA offers a different approach by verifying users, enforcing least-privilege access, and restricting connections to authorized applications. For organizations managing remote employees, cloud workloads, and third-party access, it can help reduce unnecessary exposure and strengthen access security.
Seqrite ZTNA helps organizations secure access to enterprise applications across distributed work environments through a centralized, Zero Trust-based approach. Its capabilities include granular application access control, real-time device posture checks, user-device binding, agent-based and agentless connectivity options, and visibility into user and application activity.
For businesses evaluating a VPN alternative to ZTNA, Seqrite ZTNA modernizes remote access, enforces least-privilege policies, and supports secure connectivity across on-premises and enterprise SaaS applications.
Explore Seqrite ZTNA to learn how Zero Trust access can help strengthen your organization’s remote access security.